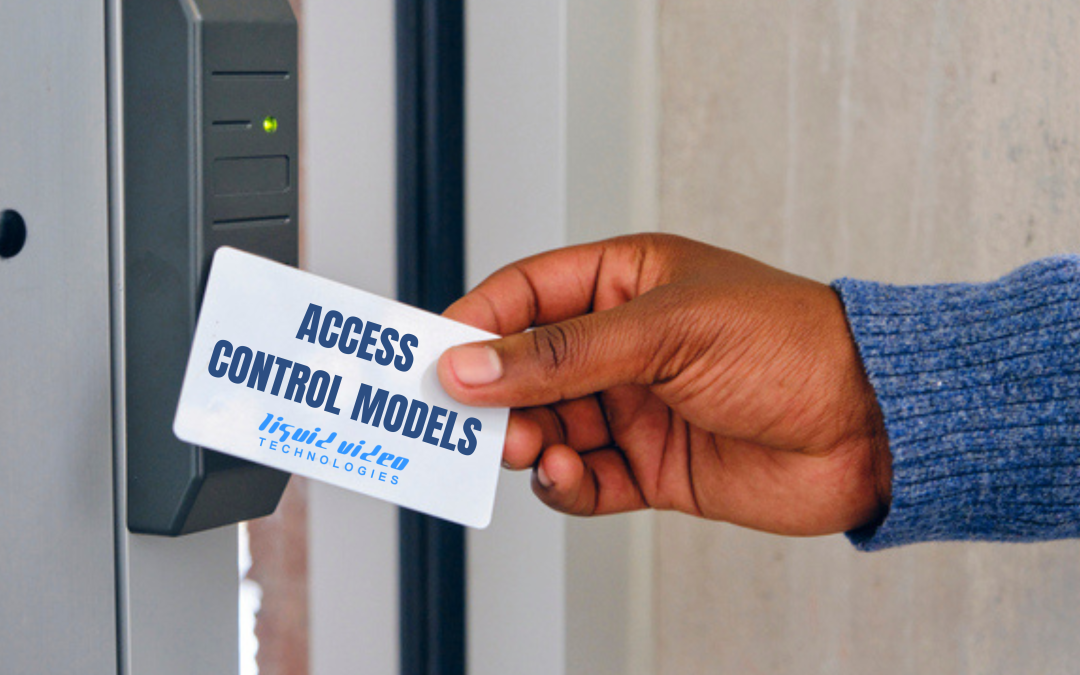
If you’ve ever researched security systems or cybersecurity for your business, you’ve probably heard the term access control. Put simply enough, access control grants your organization control over who has access to data, systems, or physical facilities. Of course any business would want to invest in such a security measure. However, while the name seems self-explanatory, there is more than meets the eye. There are five access control models that each offer different pros and cons for your business. Keep reading to learn which may be best for you.
What is Access Control?
Access control is any security measure that controls what individuals are granted access to a property, area, or interface. All access control requires that a user be able to authenticate their identity, then authorizes entry based on pre-set permissions. This may be as simple as a lock and key or computer password, or as complicated as a retinal scan or multi-factor authentication.
There are two types:
- Physical Access Control manages entry to physical locations
- Logical Access Control manages connections to digital systems such as data access, applications, and networks
Effective access control also involves audit and monitoring, in which user activity is recorded and frequently looked over by authorities. Monitoring allows the quick notice and prevention of access by an unauthorized party and can help guard against internal threats as well.
Access Control Models
There is more than one way to program access control for your property or interface. The access control models determine how access is granted to users, who has permissions to grant/revoke access, and how complicated the authentication and authorization process will be. Each of the five access control models has its own advantages and disadvantages that make them more effective for certain types of businesses than others.
Discretionary Access Control (DAC)
Discretionary access control allows multiple administrators to control access to data or a property. This means multiple people or entities can grant or revoke access/entry to users. For example, some digital interfaces such as OneDrive allow the creator of a document to control who has access to it. This gives all users some form of control over who has access to certain things.
While this mode is more simplified, organizations will have a more difficult time tracking the permissions each user has. DAC requires administrators to communicate with each other over which users should be granted access to certain interfaces, data, or areas to ensure that it is granted properly across the organization.
Mandatory Access Control (MAC)
Opposite to DAC, mandatory access control employs only one system administrator who is the sole granter of access. Users have no control over changing access themselves. Often, MAC is used by businesses who need strict security and confidentiality over their facilities or interfaces–for example, government agencies.
Role-Based Access Control (RBAC)
Role-based access control requires the creation of roles, each of which is granted different, pre-set permissions based on their responsibilities. For example, businesses may assign the HR role different permissions than a role in Sales. Employees are then labeled with their role when onboarded and automatically granted the pre-set access assigned to their role. This simplifies the process of onboarding and offboarding because each role’s permissions are already set. Instead of configuring permissions for every new employee, the administrator can simply assign them to their incoming role and all the correct permissions are automatically granted.
For example, in a residential rental in which tenants are moving in and out frequently, changing the tenant’s role is much more simplified than assigning unique permissions to every single tenant that moves in, or removing every permission from each tenant that moves out.
If not managed well, RBAC can eventually lead to role explosion if the number of roles is expanded too much. However, it is usually the best choice for most residential and standard properties due to its ability to scale up and the ease of onboarding and offboarding.
Rule-Based Access Control (RuBAC)
Rule-Based access control takes role-based access control to the next level. Rather than just authenticating a user’s role to determine access, RuBAC allows regulation of other attributes, such as controlling which times during the day users are allowed to access a certain area. For example, in an apartment complex, this could be used to limit tenants’ access to amenities after hours. In a high-security scenario, rule-based access control can be used to automatically limit access to high confidentiality areas when a breach in a different area is detected. However, because there are more variables involved in the authorization process, this type of access control is more difficult to configure.
Attribute-Based Access Control (ABAC)
Attribute-based access control evaluates multiple criteria to decide how to give access. Rather than blanket access being granted to a certain role, ABAC evaluates a few more factors once a user has authenticated themselves before granting access. For example, ABAC also considers the status of the specific file, interface, or area users are attempting to access. This can become a bit more complicated than RuBAC, but also allows for very specific control over which individuals can access which areas or data at any given time.
How do I set up Access Control?
- Choose Your Model: Decide which model will be most secure, cost-effective, and accomplishable for your business.
- Choose Your Mechanism: Determine the mechanism by which users will authenticate (for example, keycard, multi-factor authentication, etc)
- Assign Your Permissions: Configure your access control model to allow access based on the model and mechanism you chose
- Assign Authorization: Provide users with the necessary means of authenticating based on the mechanism you chose
- Automate, Monitor, and Maintain: Once the system is set up, monitor it regularly to catch any potential threats as early as possible
Access control is a valuable resource for any business that intends to protect its data and facilities from bad actors and internal threats. With a plethora of access control models available, businesses have great flexibility to improve security without completely breaking the bank. There are options for every security level, with complexity that is only limited by the time and resources you are willing to spend configuring your access control. While this may seem overwhelming, it provides the opportunity for every business to tailor access control to their own, specific needs. Companies like Liquid Video Technologies specialize in security, including physical access control. If you have any questions on how access control can benefit your business, feel free to reach out to us and we can help you determine which model is most cost effective for you.
Recent Comments